Hackers work nights.
So do we.
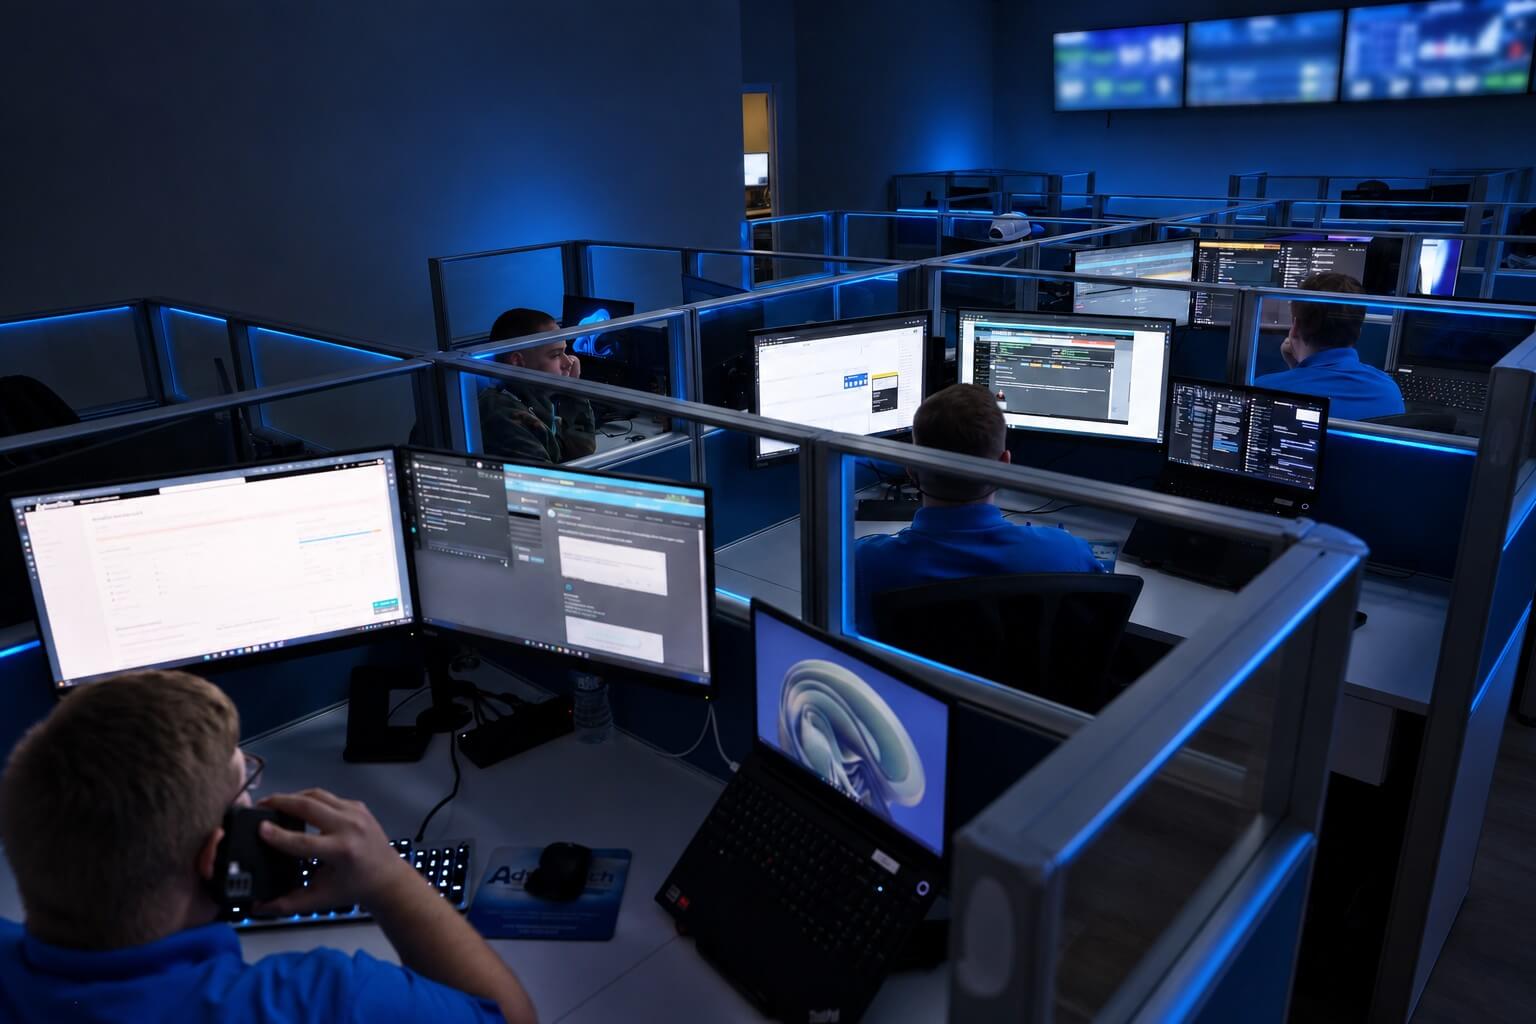
Antivirus alone doesn’t stop today’s attackers. Our managed detection and response pairs endpoint protection with a 24/7 Security Operations Center of human threat analysts who find, stop and clean up attacks around the clock.
133 Google reviews
Human analysts.
Watching 24/7/365.
Attackers love nights, weekends and holidays, when nobody is watching. Managed detection and response puts software on every workstation and server that looks for attacker behavior, then sends anything suspicious to a Security Operations Center staffed by real threat analysts, every hour of every day.
When a threat is confirmed, the device is isolated and the attacker’s footholds are removed. You get a plain-English report of what happened and what was done, and our team handles the follow-up.
- Every alert reviewed by a human analyst
- Threats isolated and remediated for you
- Satisfies cyber insurance EDR and MDR requirements
Detect. Respond.
Recover.
Endpoint Detection & Response
Continuous monitoring of every workstation and server for malicious behavior, not just known viruses.
24/7 Security Operations Center
Human threat analysts investigate and validate every alert, around the clock.
Ransomware Early Warning
Detects encryption behavior early and isolates the device before it spreads.
Persistence Hunting
Finds the hidden backdoors attackers leave behind to get back in.
Managed SIEM
Logs from firewalls, servers and cloud apps collected and correlated to catch what single tools miss.
Log Retention
Security logs kept for audits, HIPAA reviews and insurance claims.
Host Isolation & Remediation
Compromised devices cut off from the network and cleaned up, fast.
Plain-English Reporting
Monthly summaries and incident reports your leadership can actually read.
Who’s watching at 2 a.m.?
Find out with a free Cyber Security Risk Assessment.
Straight
answers.
What’s the difference between antivirus and MDR?
Antivirus blocks known threats. MDR watches for attacker behavior, and a human analyst investigates and responds when something looks wrong, including brand new attacks antivirus has never seen.
What is a SIEM and do we need one?
A SIEM collects logs from your firewall, servers and cloud apps and looks for patterns that point to an attack. It also keeps the log history auditors and insurers ask for. We manage it for you, so there is no extra tool for your staff to learn.
Will this satisfy our cyber insurance questionnaire?
Most insurers now require EDR or MDR with 24/7 monitoring. Our program covers that, and we can help you answer the questionnaire.
Let’s talk
about your IT.
Tell us a little about your organization. A real person from our Byron office gets back to you within one business day, usually much sooner.
Request a free assessment
No cost, no obligation, no pushy sales call.